The online world on high alert, again!
On 21 October, the team behind PHP released an urgent fix for two serious security flaws. PHP is the software that quietly runs behind most of the world’s websites, including every WordPress site. If you run a business website, there’s a good chance it relies on PHP.
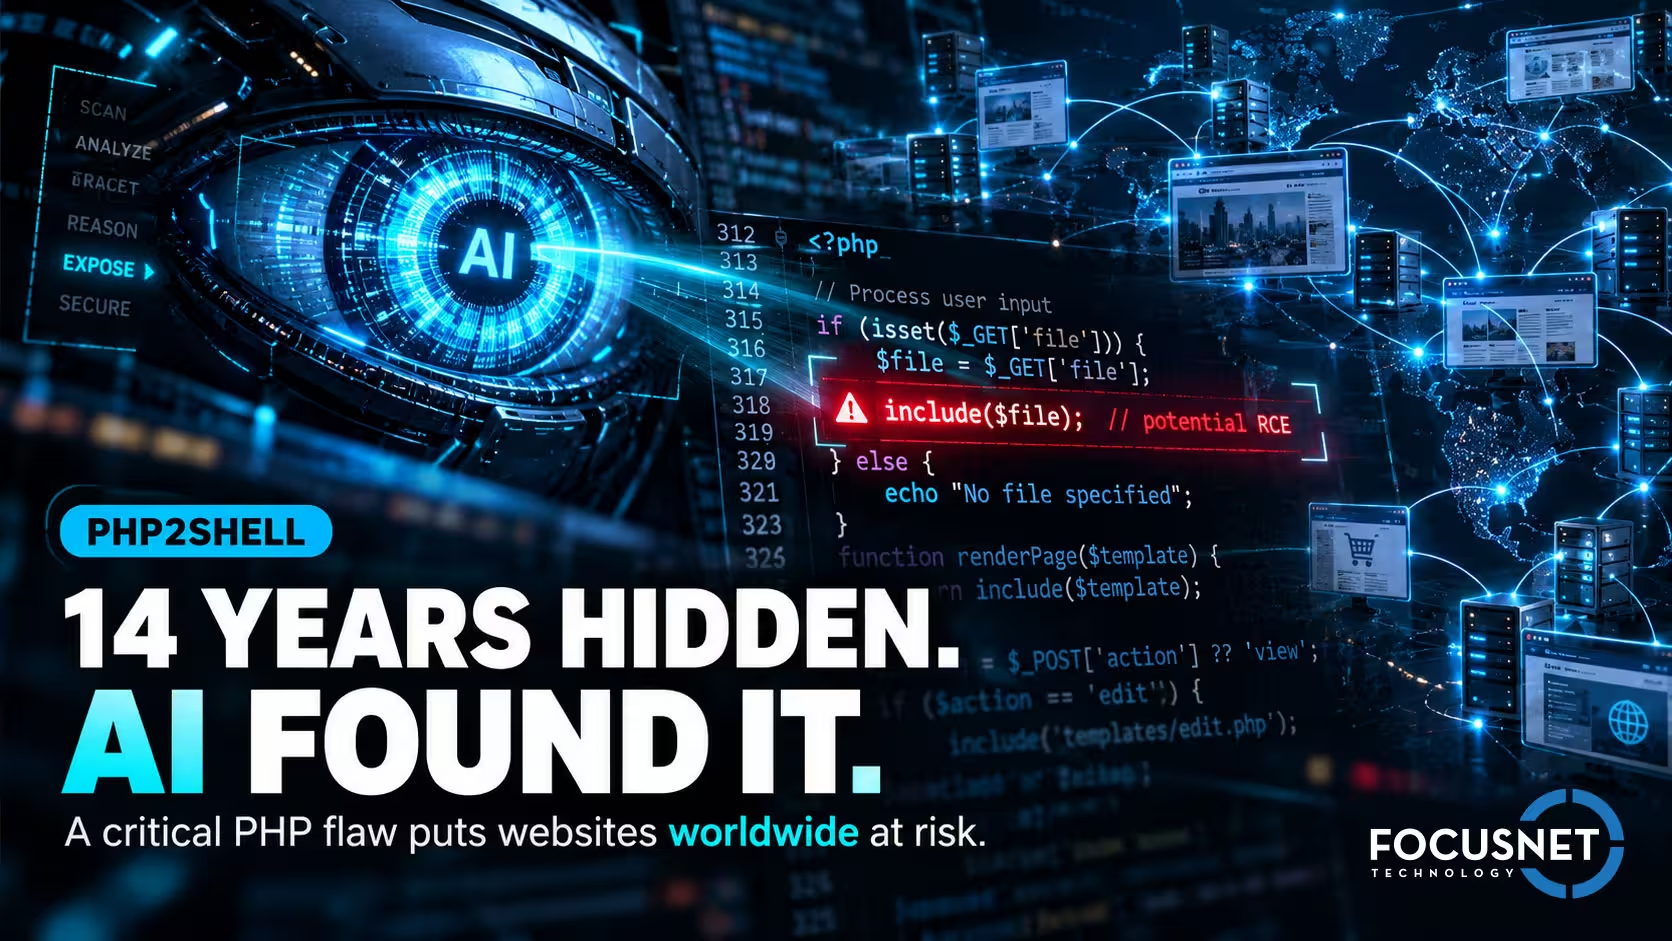
The flaws themselves are serious. But the story of how they were found is what every business owner should pay attention to. They were uncovered with the help of artificial intelligence, after part of the problem had sat in plain sight for years.
What happened?
The two flaws, nicknamed PHP2Shell (officially CVE-2026-109618 and CVE-2026-109619), could let an attacker take control of a web server without needing a password or login. Researchers confirmed it working against WordPress, Drupal, Joomla, Magento and other widely used website platforms.
The PHP project rated both flaws 9.2 out of 10 for severity. The Australian Signals Directorate took the unusual step of warning organisations before the fix was even released, telling them to get ready to update.
Things moved quickly from there. Details leaked online before the planned announcement, and attack code was published within hours. Security firms such as Hadrian and Wordfence began reporting attempts to exploit the flaws almost straight away.
The disruption reached right to the top. Australia’s own cyber security agency was among the government websites affected, with cyber.gov.au and the Australian Bureau of Statistics website both going offline overnight. The ASD said it was applying the required fix to its website, and some NSW government websites were temporarily taken down as a precaution while patches were completed.
Overseas, the response was just as dramatic. Government agencies in the Netherlands and Finland took services offline before the fix was even available, the Dutch cyber security agency switched off its own website, and France temporarily pulled local government websites. In all, government and company websites in at least a dozen countries went offline while fixes were rolled out. Most of these were precautions rather than signs of a successful attack. But when the organisations whose job is cyber security switch off their own websites, it shows how seriously the threat was taken.
A flaw hiding in plain sight
PHP is one of the most closely examined pieces of software on the internet. Security researchers have been picking through it for decades. Even the team that found these flaws said they weren’t expecting to find anything critical.
Yet according to OpenAI President Greg Brockman, the bug had been sitting in PHP’s code for around 14 years.
It wasn’t completely unknown either. In 2024, a PHP developer came across part of the underlying fault during a review. It was never fixed. The team couldn’t agree on the best way to fix it, and nobody had shown it could actually be used in an attack, so it wasn’t treated as a priority. The researchers who eventually uncovered the full flaw traced warnings about this type of weakness back even further, to 2004.
This isn’t a story about careless people. It’s a story about how hard these problems are to see. A small fault that looks harmless on its own can become dangerous when it’s combined with something else, and joining those dots across a huge, complex codebase is extraordinarily difficult for a person to do.
Why AI changes the picture
In August this year, Ryan Austin, a researcher at security firm Calif, went looking at PHP as part of OpenAI’s Patch the Planet program, set up to find and fix weaknesses in widely used software. Using one of OpenAI’s AI models to help with the analysis, he found the flaw and reported it to the PHP team. OpenAI’s own team later found a more complete version, and cloud security company Wiz found both flaws independently.
The AI didn’t do it alone. In Calif’s account of the research, Austin pointed out that his own knowledge of PHP, and where he chose to look, mattered a great deal. He also cautioned that no AI tool will find every bug.
What the AI did was help turn an overlooked, apparently harmless fault into a proven, working attack. That’s the step that had been missing for years, and it’s the step that finally got the problem fixed.
The same tools work for attackers
Here’s the uncomfortable part. If AI can help a researcher find a flaw that experienced professionals missed for years, it can help a criminal do the same.
That changes the timeline for every business with a website. The gap between a weakness being discovered and someone trying to use it is shrinking fast. With PHP2Shell, attack code was online within hours of the news breaking. And because the fix was only released for currently supported versions of PHP, websites running older versions don’t get a patch at all. They need to be upgraded.
For years, plenty of websites have been run on a set and forget basis. That approach was always risky. Now it’s a genuine liability.
What we did for our clients
We were tracking the advance warning and were ready before the fix was released. Across every web server and website we host and manage, the updates were applied within hours of release. Every site was then checked individually to confirm it was running a corrected version, and verified as loading and working normally.
If your website is hosted with FocusNet, it has been taken care of and there’s nothing you need to do.
If your website is hosted elsewhere
This issue affects any web server running PHP, no matter who manages it. If your website sits with another provider, it’s worth asking them to confirm it’s been handled. A short question is usually enough.
“Has PHP been updated on our hosting to address the vulnerabilities disclosed on 21 October 2026 (CVE-2026-109618 and CVE-2026-109619), and can you confirm the version now running?”
If you can’t get a clear answer, or you suspect your site is running an older version of PHP, we’re happy to take a look.
What this means for your business
PHP2Shell won’t be the last flaw of its kind. OpenAI has said it expects AI to turn up many more. That’s good news in the long run, because weaknesses that have hidden for years are finally being found and fixed. In the short term, it means more urgent updates, more often, with less time to act on them.
The businesses that come through this well won’t be the ones scrambling when the headlines hit. They’ll be the ones whose websites are already monitored, already kept current, and already looked after by people watching for the next warning.
That’s what we do every day for the websites we host. We monitor security advisories for the software behind them and run automated daily checks across every site, so issues are picked up and dealt with quickly, usually before anyone needs to ask. If you’d like to talk about your website’s security, get in touch with our team.
References:
- PHP, PHP news announcement, 20 October 2026
- PHP, Security advisory GHSA-w8hw-w9fx-j79w
- iTnews, Critical flaws strike PHP as disclosure embargo is broken, 21 October 2026
- Hadrian, PHP2Shell vulnerability alert
- Wordfence, Attacks on PHP2Shell continue, but no known compromises as a result yet
- ABC News, Australian government sites among those exposed to critical PHP software flaw, 22 October 2026
- Government News, Government websites taken offline, 22 October 2026
- WinBuzzer, PHP2Shell, how AI turns a stalled PHP flaw into a global emergency, 22 October 2026
- Fortune, AI tools discovered the PHP vulnerability that could take down 70% of the internet, 21 October 2026
- Decrypt, Who found the PHP bug that made governments unplug their websites?
- Wikipedia, PHP2Shell
- Calif, PHP2Shell research write-up
- explainx.ai, OpenAI on PHP2Shell
Further reading for WordPress site owners:
Wordfence, Critical PHP update and WordPress vulnerability testing